• Home
  • Blogs
  • How to Become a SOC Analyst in India (2026): Skills, Tools, Roadmap and Career Opportunities

How to Become a SOC Analyst in India (2026): Skills, Tools, Roadmap and Career Opportunities

Introduction

Starting a career in cybersecurity can feel confusing, especially when you are new to the industry. You may have heard about ethical hacking, penetration testing, cloud security and security operations, but you might not know which career path is right for you. How to Become a SOC Analyst in India – Complete Cybersecurity Career Guide One of the most practical entry points into cybersecurity is becoming a Security Operations Center (SOC) Analyst. SOC analysts help organisations protect their systems, networks, applications and cloud infrastructure from cyber threats. They monitor security alerts, investigate suspicious activities, analyse logs and support incident response teams. As businesses increasingly depend on digital platforms and cloud technologies, understanding security operations has become an important technical skill. But how do you become a SOC analyst in India? Which skills should you learn? Do you need programming knowledge? Which SIEM tools are important? And how can a fresher gain practical experience? This guide answers these questions step by step. Whether you are a student, fresher, IT professional or someone planning to switch careers, you will learn what it takes to start a career as a SOC analyst in 2026.
Quick Overview: How to Become a SOC Analyst

If you want to become a SOC analyst, focus on building these skills:

  • Understand computer networks, TCP/IP, DNS and firewalls.
  • Learn Windows and Linux operating systems.
  • Understand cybersecurity fundamentals and common cyber attacks.
  • Develop practical knowledge of SIEM platforms such as Splunk, IBM QRadar and Microsoft Sentinel.
  • Learn cloud security monitoring across AWS, Microsoft Azure and Google Cloud.
  • Understand IDS/IPS tools such as Snort and Suricata.
  • Practise security monitoring, alert investigation and incident response.
  • Build practical projects and prepare for entry-level cybersecurity certifications.

The most important thing is to combine theoretical knowledge with hands-on practice.

1. What Is a SOC Analyst?

A SOC Analyst is a cybersecurity professional responsible for monitoring, detecting, investigating and responding to potential security threats within an organisation.

SOC stands for Security Operations Center. It is a centralised team or facility where security professionals monitor an organisation’s digital environment.

Think about a bank that processes thousands of online transactions every minute. If someone attempts to access customer accounts using stolen credentials, the organisation needs to identify that activity quickly.

This is where SOC analysts play an important role.

They monitor security systems, investigate unusual activities, identify potential attacks and coordinate with other security professionals to reduce risks.

What Does a SOC Analyst Do?

A SOC analyst performs several security-related activities throughout the day.

1. Security Monitoring

SOC analysts continuously monitor security dashboards, network traffic, endpoints, servers and cloud environments to identify suspicious activities.

2. Alert Investigation

When a security tool generates an alert, the analyst investigates whether it represents a genuine threat or a false positive.

3. Log Analysis

They examine logs generated by operating systems, firewalls, applications, servers and cloud platforms to understand unusual behaviour.

4. Threat Detection

Analysts identify indicators of compromise, suspicious IP addresses, unusual login attempts, malware activity and unauthorised access.

5. Incident Response

When an incident is confirmed, analysts follow organisational procedures to contain the threat, investigate its impact and escalate it to the appropriate team.

6. Security Reporting

They document investigation findings, incident timelines, affected systems and recommended security improvements.

A Real-World Example

Imagine an employee receives a phishing email containing a malicious attachment.

The employee opens the attachment, and suspicious activity begins on their computer.

A SOC monitoring platform generates an alert.

The SOC analyst then:

  1. Reviews the security alert.
  2. Checks the affected device and user account.
  3. Examines endpoint and network logs.
  4. Identifies suspicious processes or connections.
  5. Determines whether the activity is malicious.
  6. Escalates or coordinates containment.
  7. Documents the investigation.

This is how SOC analysts help organisations respond to cybersecurity incidents.

2. Different Levels of SOC Analysts: L1, L2 and L3

SOC teams generally organise responsibilities into different tiers. The exact responsibilities vary between organisations.

SOC Analyst Level 1 – Alert Monitoring and Triage

L1 SOC analysts are generally the first point of contact for security alerts.

Their responsibilities include:

  • Monitoring SIEM dashboards.
  • Reviewing security alerts.
  • Identifying suspicious login attempts.
  • Performing initial investigations.
  • Following incident response procedures.
  • Escalating confirmed or complex incidents to L2 analysts.

This is a common starting point for freshers entering security operations.

SOC Analyst Level 2 – Incident Investigation

L2 analysts handle more detailed investigations.

  • Investigating escalated security incidents.
  • Performing log correlation.
  • Analysing malware-related activities.
  • Investigating compromised endpoints.
  • Identifying attack patterns.
  • Supporting incident containment and remediation.

SOC Analyst Level 3 – Advanced Threat Detection

L3 analysts work on complex security incidents and advanced threat investigations.

  • Advanced threat hunting.
  • Developing detection rules.
  • Analysing advanced attack techniques.
  • Performing deeper forensic investigations.
  • Improving security monitoring systems.
  • Supporting security architecture and incident response strategies.

Career tip: You do not need to master every advanced security technology before applying for your first SOC role. Start with strong networking, operating system and security fundamentals.

3. Essential Technical Skills Required to Become a SOC Analyst

You do not need to know everything about cybersecurity before starting. However, certain technical foundations are important. Networking fundamentals for SOC analysts including network monitoring and security protocols
3.1 Networking Fundamentals

Networking is one of the most important skills for SOC analysts. Security alerts often involve suspicious IP addresses, network connections, DNS requests, ports and communication between systems. You should understand:
  • IP addressing and subnetting.
  • TCP and UDP.
  • DNS and DHCP.
  • HTTP and HTTPS.
  • Common network ports.
  • Routers and switches.
  • Firewalls.
  • VPNs.
  • Packet analysis.
  • Basic network troubleshooting.
For example, if a computer communicates with an unfamiliar external IP address, a SOC analyst should understand how to investigate that connection. Recommended practical tools: Wireshark, Nmap and basic network troubleshooting utilities.

3.2 Linux Fundamentals

Linux is widely used in servers, cloud infrastructure and security environments. SOC analysts should understand basic Linux commands and how to examine system activity.
  • pwd – Display the current directory.
  • ls – List files and directories.
  • cd – Change directories.
  • cat – Display file contents.
  • grep – Search for specific text.
  • find – Locate files.
  • ps – Display running processes.
  • top – Monitor system processes.
  • chmod – Modify file permissions.
  • sudo – Execute commands with elevated privileges.
You should also learn how to examine authentication logs, identify suspicious processes and understand file permissions.

3.3 Windows Operating System Fundamentals

Many organisations use Windows-based computers, servers and enterprise infrastructure. A SOC analyst should understand:
  • Windows Event Viewer.
  • Windows Security Logs.
  • User account management.
  • Active Directory fundamentals.
  • PowerShell basics.
  • Windows Defender.
  • Login and authentication events.
  • Windows Firewall.
  • Endpoint monitoring.
For example, repeated failed login attempts can indicate password-guessing activity. Windows Event Viewer helps analysts examine events and investigate suspicious behaviour.

3.4 Cybersecurity Fundamentals

Before working with security monitoring tools, understand the basic principles of cybersecurity.
  • Confidentiality, Integrity and Availability (CIA Triad).
  • Authentication and authorisation.
  • Encryption and hashing.
  • Malware and ransomware.
  • Phishing and social engineering.
  • Vulnerability management.
  • Access control.
  • Security policies.
  • Risk management.
  • Indicators of Compromise (IoCs).
You should also become familiar with the MITRE ATT&CK framework, which provides a structured knowledge base of adversary tactics and techniques.

3.5 Cloud Security Monitoring

Modern organisations do not operate only from traditional office networks. They use cloud platforms to host applications, manage databases, store information and operate business infrastructure.

As a result, SOC analysts increasingly need to understand cloud environments.

Cloud security monitoring is an important defensive skill for modern SOC teams.

It involves monitoring cloud activity, identifying suspicious access, investigating security alerts, reviewing audit logs and detecting potential threats affecting cloud infrastructure.

Important Cloud Platforms for SOC Analysts

Amazon Web Services (AWS)

SOC analysts should understand:

  • AWS CloudTrail for recording account activity and API events.
  • Amazon GuardDuty for detecting potential threats.
  • AWS Security Hub for centralising security findings.
  • Amazon CloudWatch for monitoring and observability.

For example, an analyst can investigate unusual API activity or potentially compromised cloud credentials using relevant AWS security findings.

Microsoft Azure

Important technologies include:

  • Microsoft Sentinel.
  • Microsoft Defender for Cloud.
  • Azure Monitor.
  • Microsoft Entra ID.
  • Azure Activity Logs.

SOC analysts can use these technologies to investigate suspicious sign-ins, monitor cloud resources and review security incidents.

Google Cloud Platform (GCP)

Important technologies include:

  • Security Command Center.
  • Cloud Logging.
  • Cloud Audit Logs.
  • Cloud Monitoring.

These services help security teams review cloud activity, investigate configuration changes and monitor potential security findings.

What Should a SOC Analyst Learn About Cloud Security?

Focus on these practical skills:

  1. Understanding cloud computing fundamentals.
  2. Learning cloud IAM and access permissions.
  3. Monitoring cloud audit logs.
  4. Investigating suspicious account activity.
  5. Understanding cloud network security.
  6. Identifying misconfigurations.
  7. Monitoring security alerts.
  8. Understanding cloud incident response.

Important distinction: Cloud security is the defensive discipline of protecting cloud infrastructure, identities, workloads and data. Cloud penetration testing is an offensive security activity that assesses cloud environments for exploitable weaknesses. They are related but different skill areas.

4. SIEM Tools Every SOC Analyst Should Learn

Learning cybersecurity fundamentals is important, but SOC analysts also need practical experience with security monitoring platforms. SOC analyst using SIEM tools including Splunk and Microsoft Sentinel for security monitoring One of the most important technologies used in Security Operations Centers is SIEM.
What Is SIEM?

SIEM stands for Security Information and Event Management. A SIEM platform collects security logs and event data from different sources, analyses the information, correlates related events and generates alerts that help security teams investigate potential threats. For example, imagine an employee account experiences multiple failed login attempts followed by a successful login from an unusual location. A SIEM platform can correlate these events and generate an alert for further investigation.

Popular SIEM Tools Used in Cybersecurity

1. Splunk Enterprise Security

Splunk is a widely used data analytics and security monitoring platform. Splunk Enterprise Security provides SIEM capabilities that help security teams identify threats, investigate incidents and monitor security events. SOC analysts should understand:
  • Searching and analysing security logs.
  • Using Search Processing Language (SPL).
  • Creating dashboards.
  • Investigating security alerts.
  • Understanding correlation searches.

2. IBM QRadar

IBM QRadar is a SIEM platform that collects and analyses security events from different sources. Important learning areas include:
  • Security event monitoring.
  • Log source management.
  • Offense investigation.
  • Event correlation.
  • Security dashboards.

3. Microsoft Sentinel

Microsoft Sentinel is a cloud-native SIEM and security orchestration, automation and response (SOAR) platform. It helps organisations collect security data, detect threats, investigate incidents and automate security responses across cloud and hybrid environments. Important Microsoft Sentinel skills include:
  • Connecting data sources.
  • Understanding data connectors.
  • Writing Kusto Query Language (KQL) queries.
  • Creating analytics rules.
  • Investigating security incidents.
  • Using workbooks and dashboards.
  • Understanding automation rules and playbooks.

4. Elastic Security (ELK Stack)

Elastic Security provides SIEM and security analytics capabilities using the Elastic Stack. It helps security teams collect, search, visualise and investigate security-related data. Important concepts include:
  • Elasticsearch.
  • Logstash.
  • Kibana.
  • Data ingestion.
  • Security dashboards.
  • Detection rules.

5. Wazuh

Wazuh is an open-source security platform that provides security monitoring, threat detection, vulnerability detection and endpoint security capabilities. SOC analysts can use Wazuh to monitor endpoints, analyse security events and investigate suspicious activities.

Comparison of Popular SIEM Platforms

SIEM Tool Important Skill Application
Splunk SPL Log analysis and threat detection
IBM QRadar Event correlation Security monitoring
Microsoft Sentinel KQL Cloud-native security monitoring
Elastic Security Elasticsearch and Kibana Security analytics
Wazuh Endpoint monitoring Threat and security monitoring
Learning recommendation: Start with one SIEM platform and understand how to collect logs, investigate alerts, write basic queries and document incidents. Once you understand these concepts, learning another platform becomes easier.

5. IDS, IPS and Other Security Monitoring Tools

Along with SIEM platforms, SOC analysts should understand technologies that monitor network traffic and identify suspicious activities.

What Is IDS?

IDS stands for Intrusion Detection System.

An IDS monitors network or system activities to identify suspicious behaviour and potential security threats. It generates alerts when it detects activity that matches known attack patterns or detection rules.

What Is IPS?

IPS stands for Intrusion Prevention System.

An IPS monitors network traffic and can automatically block or prevent detected malicious activity based on configured rules.

Popular IDS/IPS Tools

1. Snort

Snort is an open-source network intrusion detection and prevention system.

It analyses network traffic and identifies suspicious activity using detection rules.

2. Suricata

Suricata is an open-source network threat detection engine that supports IDS, IPS and network security monitoring capabilities.

3. Zeek

Zeek is a network security monitoring platform that provides detailed information about network activity through structured logs.

4. Wireshark

Wireshark is a network protocol analyser used to capture and inspect network packets. It helps security professionals understand communication between devices and investigate suspicious network behaviour.

SIEM vs IDS vs IPS

Technology Main Purpose Example
SIEM Collecting and analysing security events Splunk, Microsoft Sentinel
IDS Detecting suspicious network activity Snort, Suricata
IPS Detecting and preventing malicious traffic Suricata, Snort in IPS mode
Network Analysis Inspecting network packets and traffic Wireshark
Network Monitoring Analysing network behaviour Zeek

Important: Snort is not a SIEM tool. It is an IDS/IPS technology. However, its security alerts and logs can be forwarded to SIEM platforms for centralised monitoring and investigation.

6. Understanding the Cybersecurity Incident Response Process

Detecting a security alert is only one part of a SOC analyst’s job. They must also understand how to investigate and respond to potential security incidents.

Incident response is a structured process used by organisations to identify, manage, contain and recover from cybersecurity incidents.

Important Incident Response Stages

1. Preparation

Organisations prepare security policies, monitoring tools, response procedures and incident handling teams before an attack occurs.

2. Detection and Analysis

Security teams identify suspicious activity, investigate alerts and determine whether a security incident has occurred.

3. Containment

The team takes appropriate action to limit the spread and impact of an incident. This may include isolating affected endpoints or disabling compromised accounts.

4. Eradication

The organisation removes the root cause of the incident, such as malware, malicious accounts or compromised access.

5. Recovery

Systems and services are restored securely, and monitoring continues to identify any further suspicious activity.

6. Lessons Learned

The security team documents the incident, reviews the response and identifies improvements to prevent similar incidents.

Understanding these stages helps SOC analysts investigate incidents systematically rather than simply closing alerts.

7. Practical SOC Analyst Projects to Build Your Experience

One of the biggest challenges for cybersecurity beginners is gaining practical experience. SOC analyst career roadmap from beginner to professional cybersecurity specialist Employers want candidates who understand how security tools work in real situations. Therefore, working on practical projects can help you demonstrate your technical knowledge.
Project 1: SIEM Log Monitoring and Investigation

Set up a SIEM lab using Splunk, Wazuh or Microsoft Sentinel and practise analysing security events. What you will learn:
  • Collecting system and security logs.
  • Creating basic monitoring dashboards.
  • Searching for suspicious activities.
  • Investigating security alerts.
  • Documenting investigation results.

Project 2: Failed Login Detection

Build a monitoring exercise that identifies repeated failed login attempts from Windows or Linux authentication logs. What you will learn:
  • Authentication log analysis.
  • Identifying suspicious login patterns.
  • Creating detection queries.
  • Generating security alerts.

Project 3: Phishing Email Investigation

Analyse a safe phishing email sample in an isolated learning environment. What you will learn:
  • Examining email headers.
  • Identifying suspicious URLs.
  • Understanding sender authentication.
  • Analysing indicators of compromise.
  • Preparing an incident report.

Project 4: Cloud Security Monitoring

Create a cloud security monitoring lab using AWS, Microsoft Azure or Google Cloud. What you will learn:
  • Understanding cloud audit logs.
  • Monitoring cloud account activity.
  • Reviewing identity and access events.
  • Identifying suspicious cloud activity.
  • Investigating cloud security findings.

Project 5: Network Traffic Analysis

Use Wireshark to capture and analyse network traffic in an authorised lab environment. What you will learn:
  • Understanding network protocols.
  • Examining DNS requests.
  • Analysing TCP connections.
  • Identifying unusual network communication.
  • Preparing network investigation reports.
Pro tip: Document every project with its objective, tools used, investigation steps, screenshots and findings. You can use these projects to demonstrate your practical knowledge during interviews.

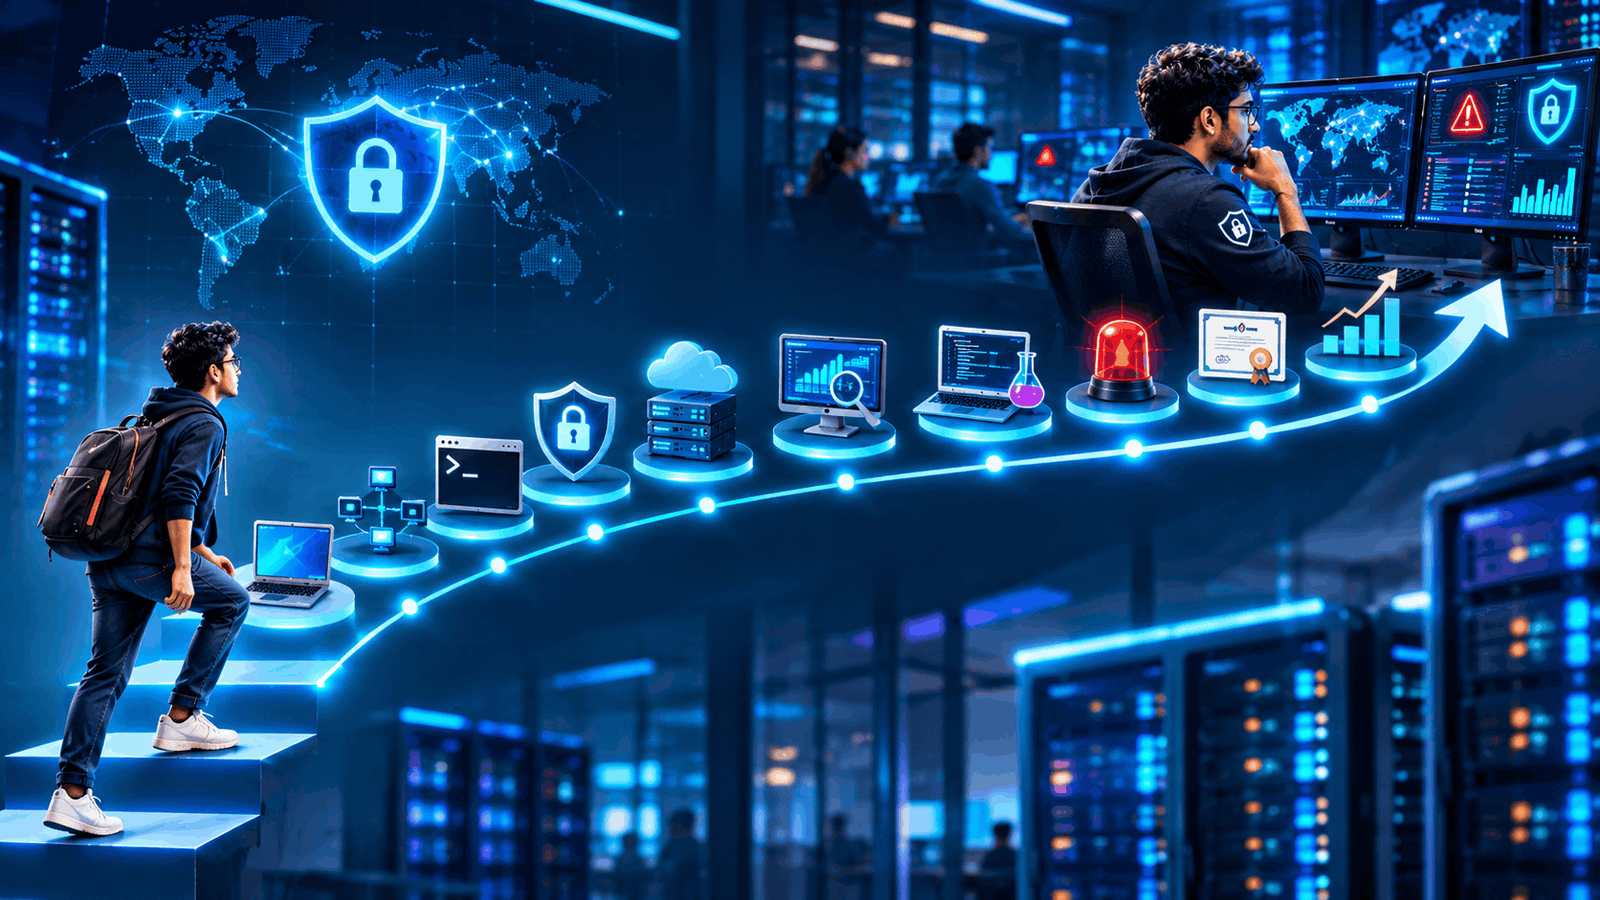
8. SOC Analyst Career Roadmap for Beginners

If you are starting from zero, following a structured learning roadmap can help you build your cybersecurity knowledge step by step.

Step 1: Learn Computer Fundamentals

Understand computer hardware, operating systems, files, processes, memory and basic troubleshooting.

Step 2: Learn Networking

Study TCP/IP, DNS, DHCP, HTTP, HTTPS, IP addressing, ports, firewalls and network communication.

Step 3: Learn Linux and Windows

Practise Linux commands, Windows Event Viewer, system logs, PowerShell and basic system administration.

Step 4: Understand Cybersecurity Fundamentals

Learn malware, phishing, ransomware, authentication, encryption, vulnerabilities and common attack techniques.

Step 5: Learn SIEM Platforms

Practise using Splunk, Microsoft Sentinel, IBM QRadar, Elastic Security or Wazuh. Focus on log collection, alert investigation and detection queries.

Step 6: Understand Cloud Security

Learn AWS, Azure and Google Cloud fundamentals, cloud identity management, audit logs, monitoring and security alerts.

Step 7: Practise With Security Labs

Build practical projects involving log analysis, phishing investigation, network monitoring and incident response.

Step 8: Prepare for Certifications

Choose relevant entry-level cybersecurity certifications based on your learning objectives and career plans.

Step 9: Prepare for SOC Analyst Interviews

Practise technical questions, explain your projects, understand common security scenarios and prepare to demonstrate your investigation skills.

Remember, consistency and practical experience are more valuable than simply collecting certificates.

9. Best Certifications for Aspiring SOC Analysts

Certifications can help you demonstrate your cybersecurity knowledge and provide structured learning objectives.

Here are some certifications worth considering:

1. CompTIA Security+

CompTIA Security+ covers cybersecurity fundamentals, threats, vulnerabilities, security architecture, risk management and security operations.

2. CompTIA Network+

This certification focuses on networking concepts, infrastructure, network operations, troubleshooting and network security.

3. Microsoft Security Operations Analyst Associate (SC-200)

The SC-200 certification focuses on security operations, threat investigation, incident response and Microsoft’s security technologies, including Microsoft Sentinel and Microsoft Defender.

4. Certified SOC Analyst (CSA)

EC-Council’s Certified SOC Analyst certification focuses on security monitoring, threat detection, SIEM operations and SOC processes.

5. Blue Team Level 1 (BTL1)

Blue Team Level 1 focuses on defensive security skills, including security monitoring, phishing analysis, digital forensics and incident response.

Important: Certifications are not mandatory for every SOC analyst position. Employers may also evaluate practical skills, technical knowledge, lab experience and problem-solving abilities.

10. SOC Analyst Salary in India

SOC analyst salaries in India depend on several factors, including experience, technical skills, organisation, location and the complexity of the role.

Professionals with practical experience in SIEM platforms, cloud security monitoring, threat detection and incident response may have opportunities to progress into specialised security roles.

Career Opportunities in SOC Operations

  • SOC Analyst L1
  • SOC Analyst L2
  • SOC Analyst L3
  • Security Monitoring Analyst
  • Incident Response Analyst
  • Threat Intelligence Analyst
  • Cloud Security Analyst
  • Security Engineer
  • Security Operations Engineer
  • Security Architect

What Influences SOC Analyst Salary?

  • Practical SIEM experience.
  • Knowledge of Microsoft Sentinel and Splunk.
  • Cloud security knowledge.
  • Incident investigation skills.
  • Networking and operating system fundamentals.
  • Relevant certifications.
  • Communication and documentation skills.

Instead of focusing only on salary figures, beginners should concentrate on building practical skills and developing a strong technical foundation.

11. Why Should You Choose a SOC Analyst Career?

Cybersecurity offers several career opportunities for people interested in technology, problem-solving and digital security.

1. Entry Point Into Cybersecurity

SOC analyst roles can provide a structured starting point for people interested in defensive cybersecurity.

2. Practical Technical Experience

You gain exposure to security monitoring, operating systems, networking, SIEM platforms and incident investigation.

3. Opportunities Across Industries

Banks, healthcare organisations, IT companies, government departments, consulting firms and cloud service providers need security professionals.

4. Multiple Career Progression Options

With experience, you can explore specialised roles in incident response, threat hunting, cloud security, security engineering and security architecture.

5. Continuous Learning

Cybersecurity constantly evolves. You get opportunities to learn about new threats, technologies, tools and security practices.

Start Your Cybersecurity Career With the Right Training

Becoming a SOC analyst requires more than understanding cybersecurity terminology. You need a strong technical foundation, practical experience with security monitoring tools and the ability to investigate real-world security scenarios. SOC analyst career roadmap from beginner to professional cybersecurity specialist Start with networking, Linux, Windows and cybersecurity fundamentals. Then develop your knowledge of SIEM platforms, Microsoft Sentinel, cloud security monitoring and incident response. If you want structured guidance, practical lab experience and a deeper understanding of cybersecurity, explore the Masters Program in Cyber Security by BinaryBrains. Speak with our career advisor to understand the programme curriculum, practical training, batch details and career opportunities. Take the first step towards building your cybersecurity career. Explore Masters Program in Cyber Security → Book Free Career Counselling →
12. Frequently Asked Questions About Becoming a SOC Analyst

1. Can a fresher become a SOC analyst in India?

Yes. Freshers can apply for entry-level SOC analyst positions. However, they should develop networking, Linux, Windows, cybersecurity and SIEM fundamentals and gain practical experience through labs and projects.

2. Is coding required to become a SOC analyst?

Advanced programming is not mandatory for every entry-level SOC position. However, basic scripting knowledge in Python, PowerShell or Bash can help automate tasks, analyse logs and investigate security incidents.

3. Which SIEM tool should beginners learn first?

Beginners can start with Splunk, Microsoft Sentinel or Wazuh. Focus on understanding log collection, queries, alert investigation and incident handling before moving to advanced platforms.

4. Is Microsoft Sentinel a SIEM tool?

Yes. Microsoft Sentinel is a cloud-native SIEM and SOAR platform used for security monitoring, threat detection, incident investigation and automated response.

5. Is Snort a SIEM tool?

No. Snort is an open-source Intrusion Detection and Prevention System (IDS/IPS). It analyses network traffic to detect suspicious activities. Its alerts can be integrated with SIEM platforms for centralised security monitoring.

6. Should SOC analysts learn cloud security?

Yes. Cloud security knowledge is increasingly useful because organisations use AWS, Microsoft Azure and Google Cloud. SOC analysts should understand cloud logs, identity management, monitoring and threat detection.

7. What is the difference between SOC analyst and ethical hacker?

A SOC analyst primarily focuses on defensive security, monitoring, threat detection and incident response. An ethical hacker performs authorised security assessments to identify vulnerabilities and demonstrate potential attack paths.

8. How long does it take to learn SOC analyst skills?

The learning duration depends on your existing technical knowledge, learning schedule and practical experience. Beginners should follow a structured roadmap covering networking, operating systems, cybersecurity, SIEM and practical labs.

9. Which certifications are useful for SOC analysts?

Some relevant certifications include CompTIA Security+, Microsoft SC-200, EC-Council Certified SOC Analyst and Blue Team Level 1. Choose certifications according to your career goals and current skill level.

10. Can non-IT students become SOC analysts?

Yes. Students from non-IT backgrounds can pursue cybersecurity by first learning computer fundamentals, networking, operating systems and security basics. Consistent practical training is important.

11. What is the difference between SIEM and IDS?

SIEM platforms collect and correlate security events from multiple sources to help investigate threats. IDS technologies monitor network or system activity and identify suspicious behaviour. Both can work together in a SOC environment.

12. What is the difference between cloud security and cloud penetration testing?

Cloud security focuses on protecting cloud infrastructure, applications, identities and data. Cloud penetration testing is an authorised offensive security assessment that identifies exploitable weaknesses in cloud environments.

Comments are closed

Enquire About No-Cost EMI
Get details about No-Cost EMI, monthly installments, bank eligibility, and payment options.

🔒 Your data is safe. No spam, ever.

Enquire About the Internship
Get details about internship fees, duration, live projects and mentor support. 

🔒 Your data is safe. No spam, ever.
Please confirm your details